-

Network Rack Security
This refers to the measures to protect a data center's servers and other IT equipment. Physical security measures aim to prevent unauthorized data. Security is a fundamental requirement in data centers and processing facilities, with recent high-profile data breaches and losses ensuring that the focus is greater than ever. Rack Security Best Practices: Control Access at the Rack Level: Deploy electronic cabinet locks to prevent unauthorized entry. What is a Networking Rack? A networking rack, often referred to as an equipment rack, stands as a. That means deploying more devices and managing larger enterprise-to-edge networks to enable digital experiences for workers and consumers. However, this fast-paced growth has come at a cost: the security of distributed networks.
[PDF Version]
-

Improve network security equipment
There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Build a vulnerability management program. Whether you're securing your Wi-Fi, enhancing device protection, or monitoring network activity, these tips will empower you to create a robust and secure home network. In this post, we'll look at a variety of common network security devices and explore how they can be used to keep your company's network safe.
-
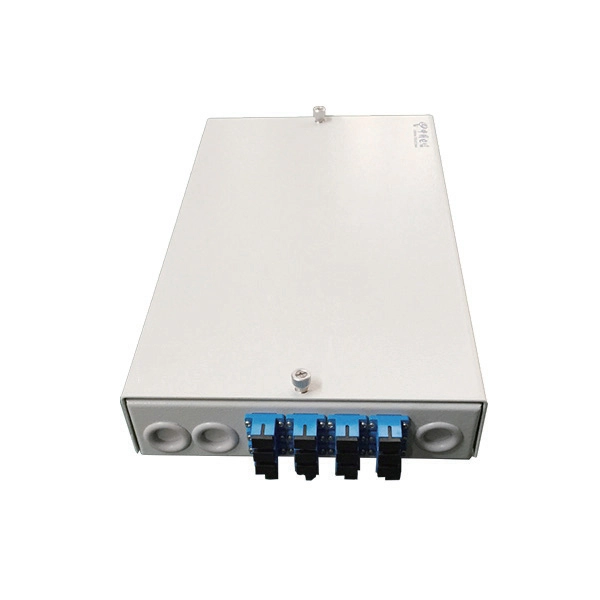
What is a network security control cabinet
“A network cabinet is a metal shelter used for apprehending networking devices like routers, switches, patch panels and servers. ” Such enclosures assist you in systematizing as well as securing the crucial elements of a network infrastructure in a safe, secure, and efficient way. Different forms. Network cabinets are the backbone of modern IT infrastructure — organizing routers, switches, servers and wiring into secure, cool, manageable racks that enable scalability, efficiency, and hardware protection. Networks are fundamental to the operation, security and resilience of many organisations. The system is scalable, integrates with DCIM and BMS software, and supports electronic handles from popular cabinet access control manufacturers.
[PDF Version]
-
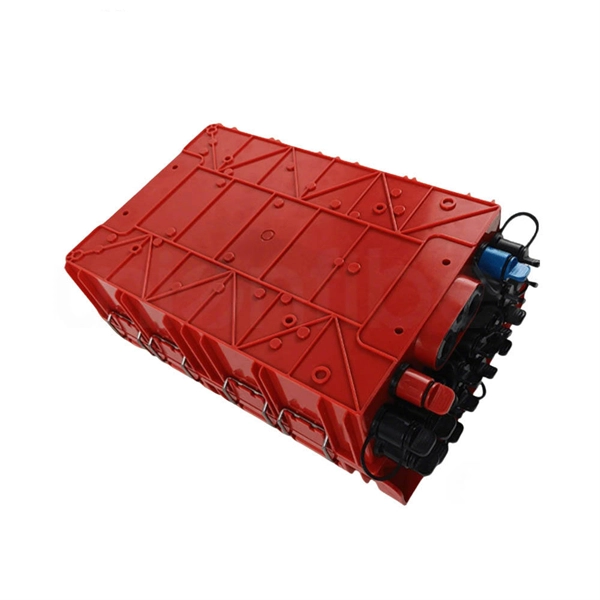
GPON user terminal device AN5506-01-A
The AN5506-01-A is a GPON bridging-type ONT. It uses the GPON technology to realize ultra-broadband access, and ensures the user experience of voice, data and HD video services. The equipment is small and easy to deploy. Figure 1-1 Network diagram of the AN5506-01-A As shown in Figure 1-1, the AN5506-01-A is used together with the AN5516-01 (OLT). They together make up a GPON system that provides a large-capacity, high-reliability multi-service access network. It provides users with communication and entertainment services in the form of data, voice, video, and so on, to meet the integrated access demand of families and small-scaled enterprises. Single Ethernet Port: Typically equipped with a single Gigabit Ethernet (GE) port. Table 2.
[PDF Version]
-
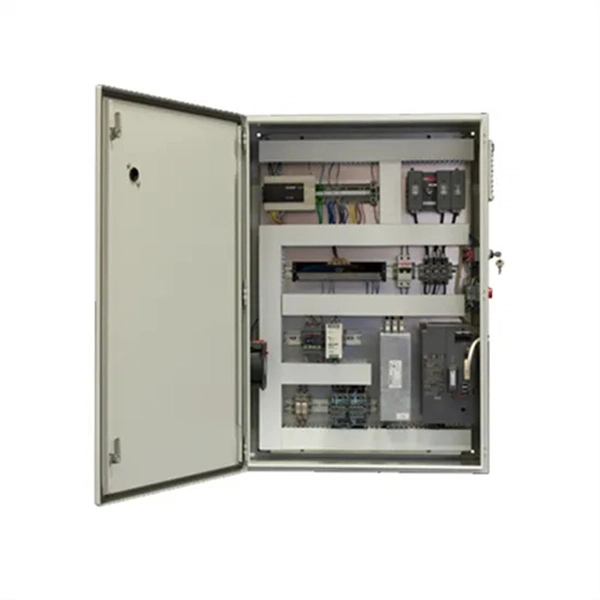
Energy-Saving Customization Process for Emergency Communication User External Distribution Boxes
Customize dimensions and mounting options to enhance ventilation, heat dissipation, and overall system efficiency based on installation requirements. Add functional enhancements, such as viewing windows and grounding points, to improve safety and operational efficiency in diverse. Emergency Power System: NEC Article 700 specifies electrical safety requirements for circuits and equipment that must operate to enable the evacuation of buildings where large numbers of people assemble, such as hotels, theaters, areas, and healthcare facilities. Circuits and equipment that provide. Distribution boxes are commonly used across various sectors such as industrial, commercial, residential, and municipal areas. The real concern is everything the box must quietly solve. Manufacture custom made Local Control Stations & Distribution Boxes, local control panel boards and stations, explosion protected control units, distribution. Utilize modular assembly in design to allow flexible configurations and ease of maintenance for future upgrades.
[PDF Version]
-
GPON user terminal device optical signal light
Optical Line Terminal (OLT) - Device that aggregates all optical signals from ONTs into a single multiplexed beam of light which is then converted into an electrical signal, formatted to Ethernet packet typ.
-

Is the optical splitter located at the user end
A single optical fiber from the OLT connects to a passive optical splitter that is located near an end user's premises. The number of optical paths can vary from 2 to 128. The common architecture of FTTH consists of the Optical Line Terminal (OLT) located in the central office, the Optical Network Unit (ONU) at the user end, and the Optical Distribution Network (ODN) in between. In the backbone layer, installation points include primary optical junction boxes, secondary optical junction boxes, or inside optical fiber.
-
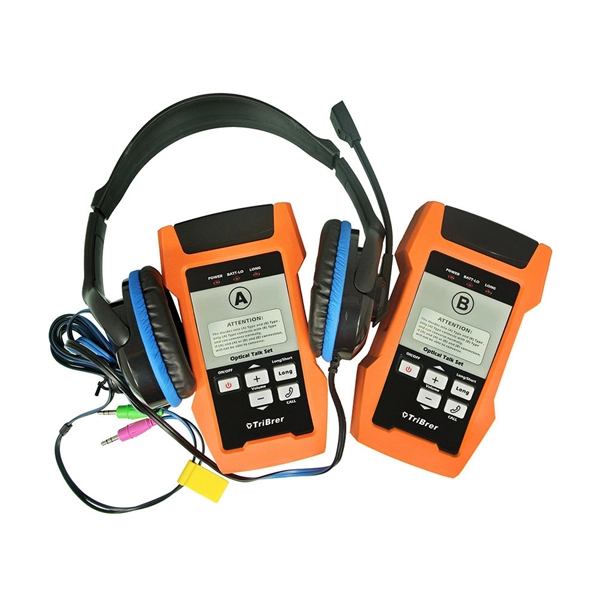
How many cores are tested in the user s optical cable
For most setups, cables with 12, 24, or 48 cores are common choices, ensuring compatibility with modern equipment and ease of management. The total number of cores for a 1pc fiber patch cable is calculated as the number of branches multiplied by the number of cores per branch (if there are no branches, the number of branches = 1). This post will guide you through understanding fiber optic cores and selecting the perfect cable for your needs. Single-mode: A. Common fiber cores include 1 core, 2 cores, 6 cores, 8 cores, etc. This differs from copper cabling, which relies on electrical pulses to move data.
-
Network Security Devices and Principles
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. They include firewalls, intrusion prevention systems, VPN gateways, and other tools that safeguard data across network. Networks are fundamental to the operation, security and resilience of many organisations. This guidance provides an introduction to the key topics to consider when designing, maintaining, or using networks that need to be secure and resilient. It ensures systems remain confidential, available, and trustworthy across all digital environments. Its features are: Network security works through multiple protective layers that control. Understand essential principles of network security, covering risk management, encryption, firewalls, and security policies to protect data. Are you worried about hackers stealing your data or breaking your systems? Many people and businesses face problems online, lost files, computer crashes, or.
[PDF Version]
-
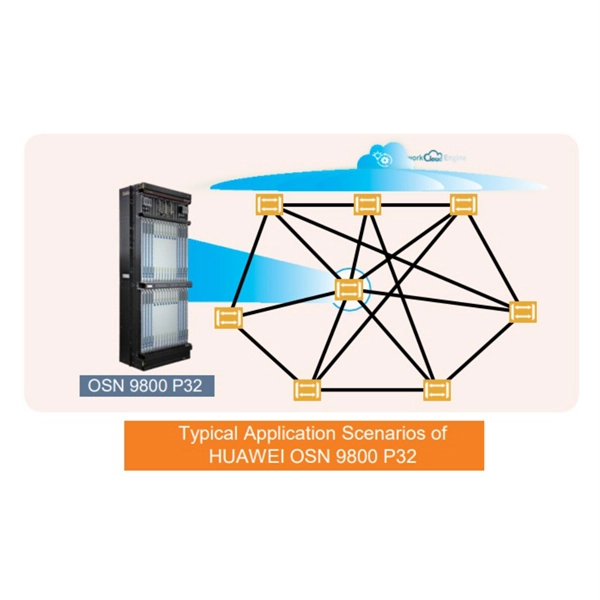
NIPS network security devices
A Network Intrusion Prevention System (NIPS) is a proactive security appliance or software solution that monitors network traffic for malicious activity and automatically takes action to block or prevent those threats in real-time. IPS typically logs data pertaining to observed events, notifies. Along this rocky road, Network Intrusion Detection and Prevention Systems (NIDS / NIPS) became an enterprise best practice–now widely considered essential at the network edge as well as at key junctions leading to high-value, [. ] Enterprise Networking Planet content and product recommendations are. A network-based intrusion prevention system (NIPS) is a type of security solution that is designed to protect networks by monitoring and analyzing network traffic in real-time for signs of malicious activity. When sketchy traffic shows up (and it always does), the system shuts it down in milliseconds. Think of NIPS as that security guard who never needs. NIDS/NIPS stands for Network Intrusion Detection System/Network Intrusion Prevention System. By following this plan, you can easily do full security checks, find vulnerabilities in your network's defences, and put.
[PDF Version]
-

DCS network security equipment
Comprehensive server protection providing visibility, compliance, hardening, and management. Automated threat response with out-of-the-box recipes to protect against critical vulnerabilities and unauthorized a.